If you’ve ever tried to bring a new tool into your business, you’ll know the moment. Everyone’s keen and the trial went well. Then someone from IT or finance asks the question that stops everything: “How do we know our data is safe with these people?”
With AI tools that question carries extra weight, because you’re connecting agents to your CRM, your inbox and your client files. It’s a fair thing to ask. Until now, the best we could do was walk you through how we’ve built Autohive and ask you to take our word for it.
Now you don’t have to. The Autohive platform has completed its SOC 2 Type 2 audit, and the result came back clean.
What SOC 2 Type 2 actually means
SOC 2 is an independent audit framework created by the American Institute of Certified Public Accountants. It’s the standard IT and procurement teams around the world look for when they decide whether a software provider can be trusted with their data.
There are two types. A Type 1 report checks that a company has the right controls in place on a single day. A Type 2 report goes further and tests whether those controls actually worked, day in and day out, over a period of time. We went for Type 2 because a security policy sitting in a folder doesn’t protect anyone. What matters is whether it gets followed.
Our audit was carried out by Insight Assurance, an independent audit firm, and it tested the Autohive platform between April and June 2026. No exceptions were noted in any of the controls tested. The audit covers the Autohive platform itself, while our marketing website, docs site and mobile apps sit outside its scope.
All five categories, not just one
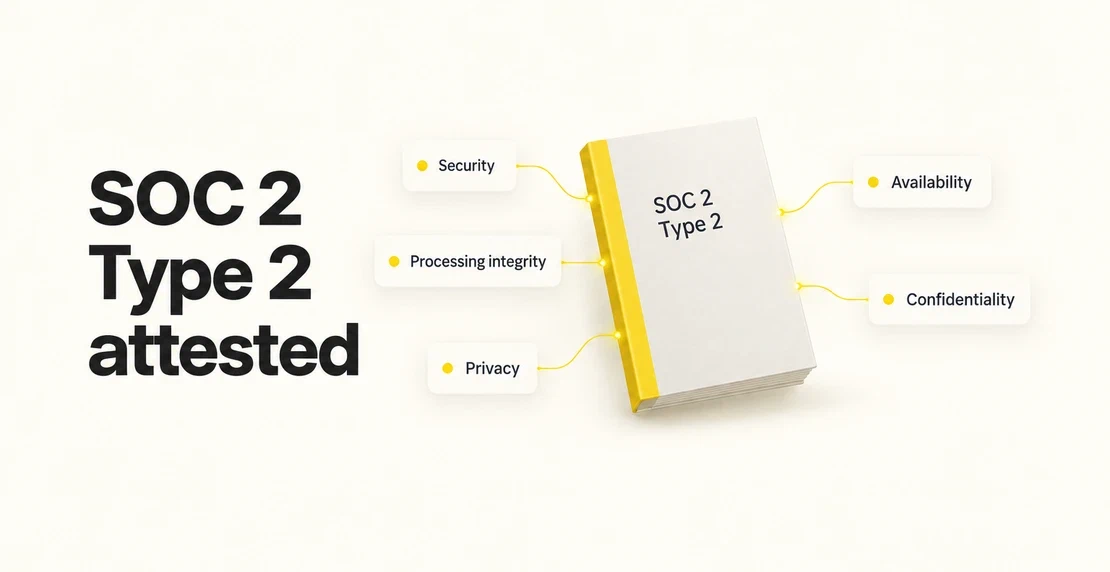
SOC 2 audits measure a company against up to five trust services categories, and we were audited against all five:
- Security. Controls designed to protect your data from unauthorised access, including multi factor authentication, encryption at rest and in transit, and continuous threat monitoring.
- Availability. Daily backups, live monitoring and a disaster recovery plan that’s tested at least once a year, to help keep the platform available when you need it.
- Processing integrity. The platform checks inputs, confirms that completed agent runs match the tasks you scheduled, and alerts our team, and notifies you, when errors occur in data transfers or scheduled runs.
- Confidentiality. Confidential information is used only for the purposes set out in our agreements with you.
- Privacy. Personal information is collected, used and handled in line with our Privacy Policy.
What this means for you
If you run a business, the security conversation with your IT person or your board can now start from an independent auditor’s report rather than a blank page.
If you run an agency and a client asks who’s checking the tools you use on their account, you have a solid answer: an independent audit firm has tested our controls.
If you work in a larger organisation where procurement has the final say, SOC 2 Type 2 is often something that has to be in place before a conversation can even begin. We can now share our report with you under NDA.
How to get the report
SOC 2 reports are confidential by design, because they contain detail about how our systems are protected. We share ours with customers and prospective customers under NDA, and you can request access at trust.autohive.com.
This is a standard we keep, not one we reached once
Staying SOC 2 attested means being audited again, so the controls tested this time have to keep working every day in between. You can see more about how we protect your data on our security page.
If security has been the thing holding your team back from trying AI agents, it doesn’t need to be anymore. Start free or talk to our team about what Autohive could take off your plate.

Jono Nourse